

October 7th, 2026
Deepfake Fraud: What Maryland Businesses Should Do Now
Posted in: Business Law Tagged: Andrew L. Schwartz
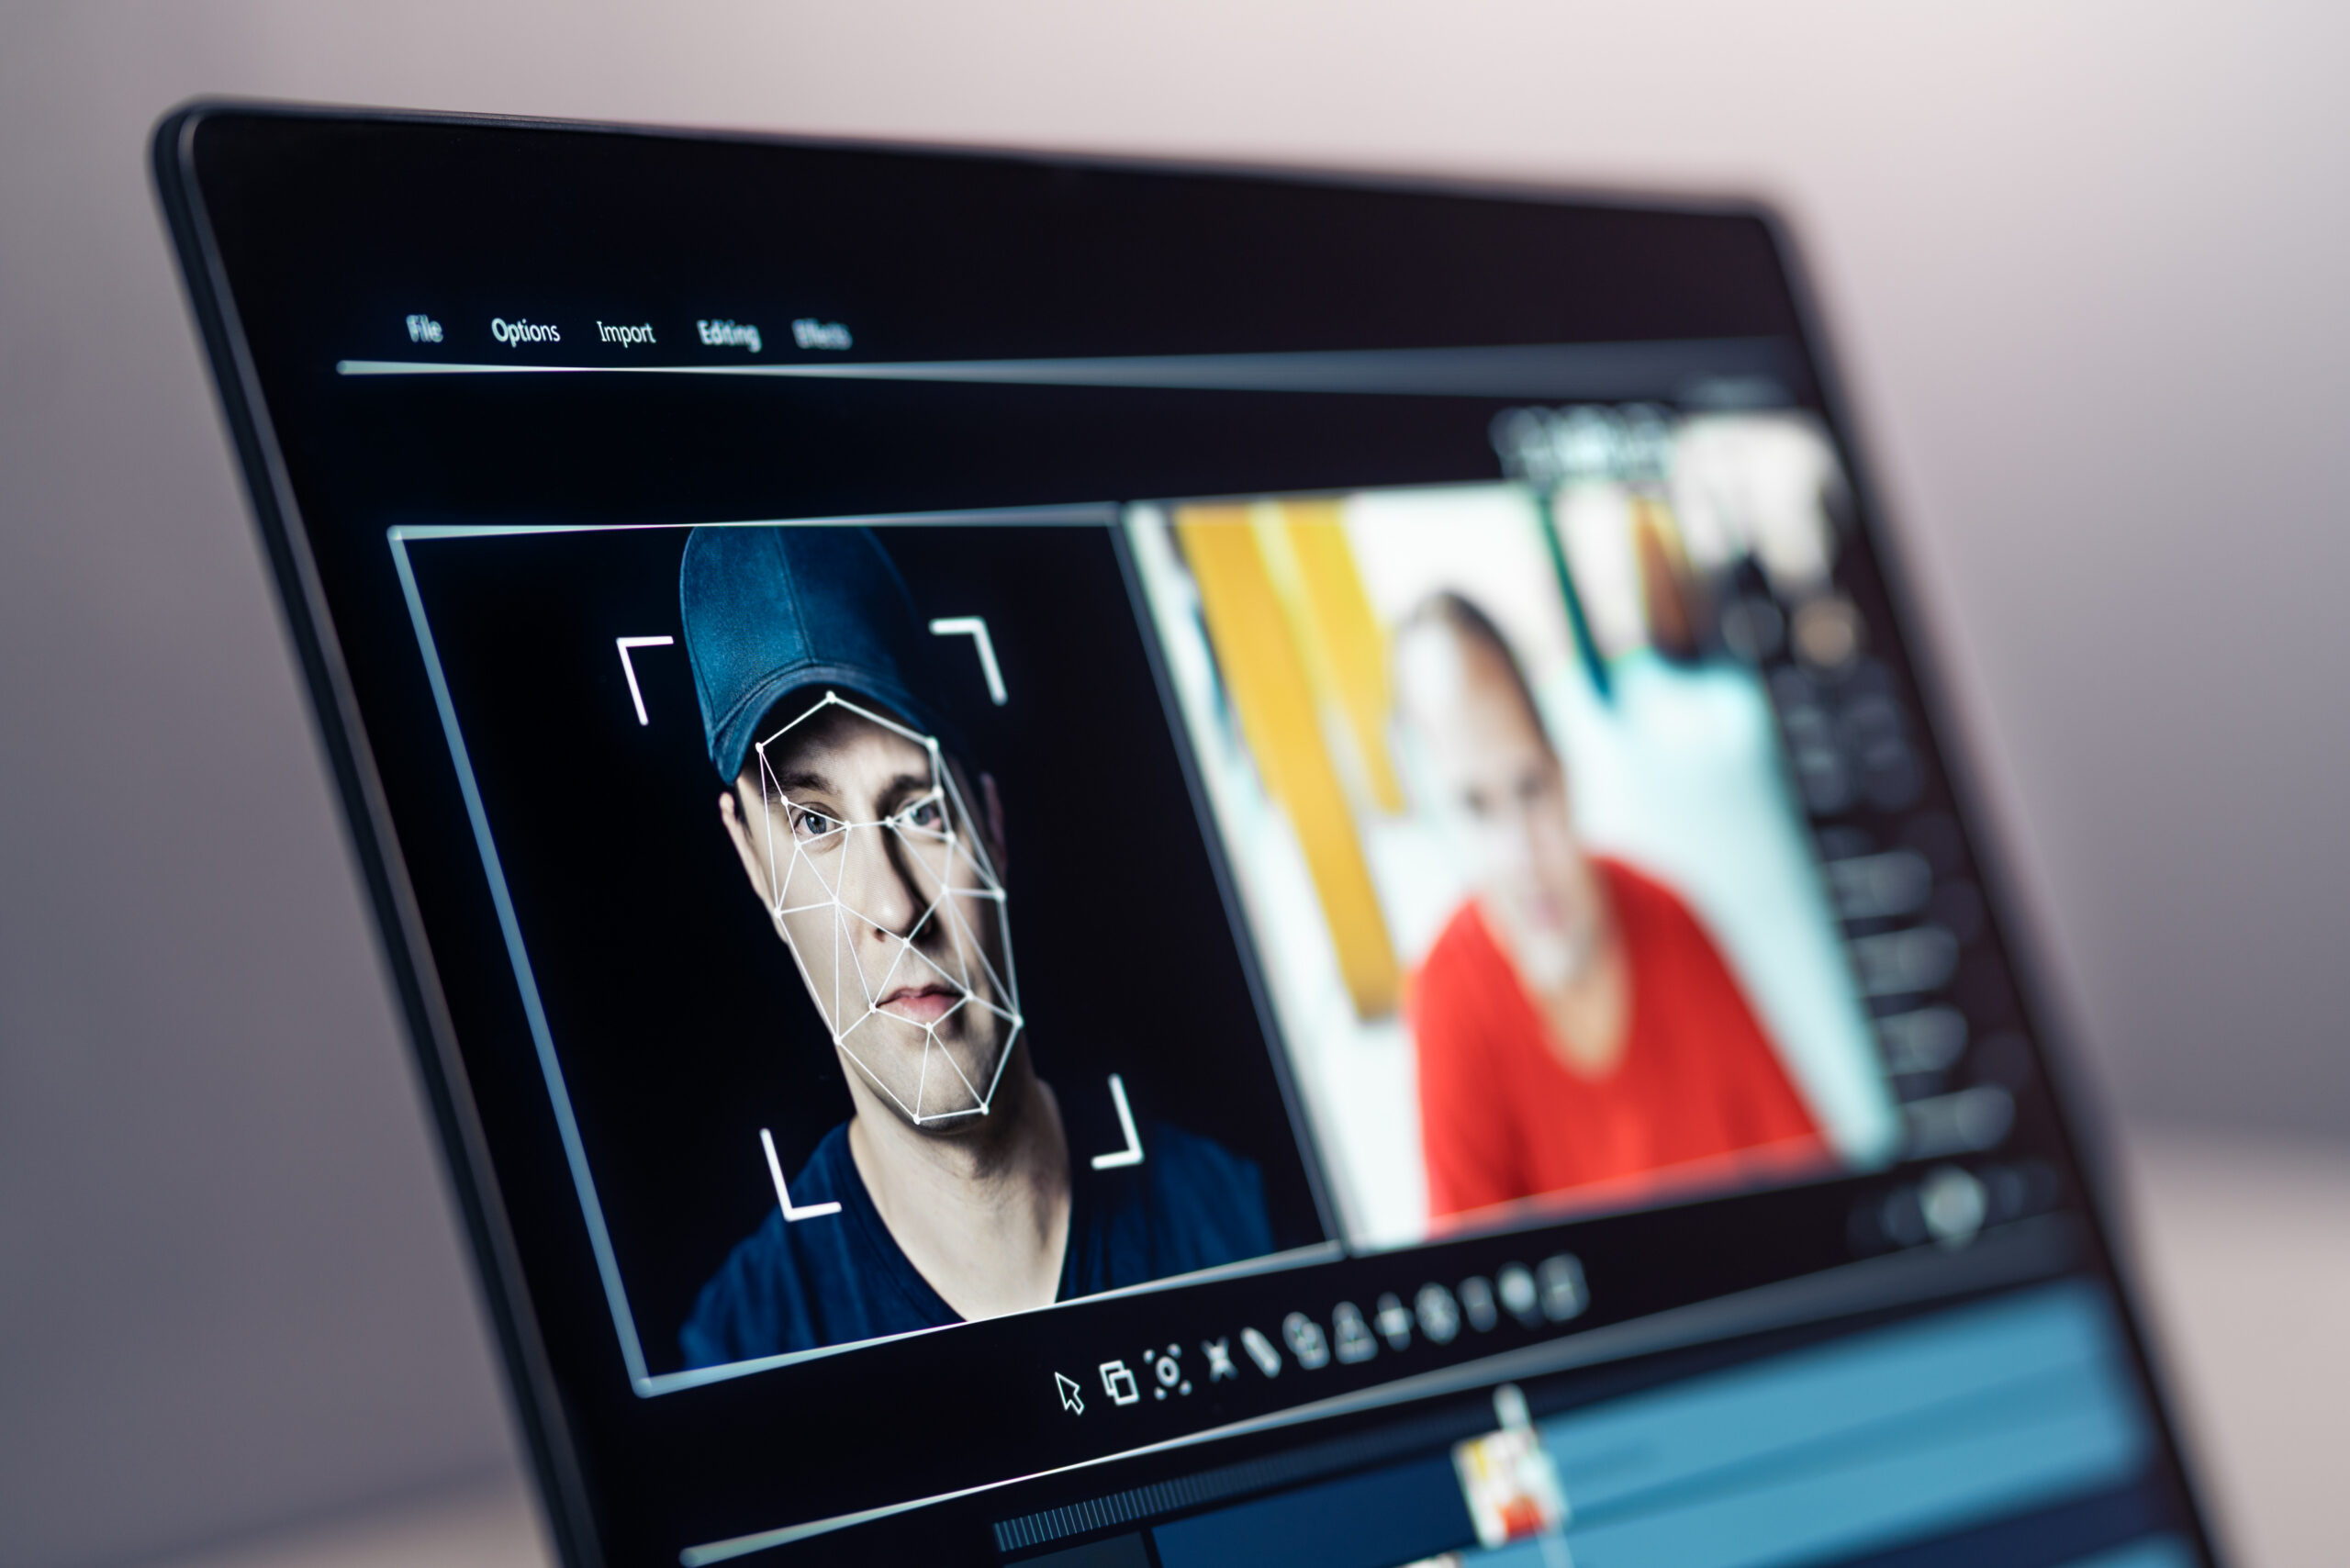
Maryland’s new deepfake law takes effect October 1, 2026. Here’s what organizations need to know to protect themselves from AI-enabled impersonation fraud.
On October 1, 2026, Maryland’s new law addressing AI-enabled identity fraud takes effect. The law prohibits knowingly and willfully using AI or deepfake technology with fraudulent intent to impersonate or falsely depict an actual person to cause harm, commit fraud, or secure unauthorized benefits. Violations are classified as felonies, and victims may pursue civil claims for injunctive relief and damages.
By the time an organization discovers that an employee was deceived into sending money, changing payment information, or disclosing sensitive data, recovery is often difficult. That makes prevention as important as the new legal remedies.
The good news: some of the most effective protections are not expensive cybersecurity tools but relatively simple procedures designed around how impersonation fraud actually works.
Why Deepfake Fraud Works
Most successful impersonation schemes rely on a combination of three elements:
Authority. The request appears to come from someone the employee is accustomed to following—a CEO, CFO, managing partner, senior executive, or long-time client.
Urgency. The transaction must happen immediately. A closing is imminent, a vendor needs payment, a deal will fall apart, or the executive is about to board a plane.
Single channel. The entire transaction occurs through one email chain, text exchange, phone call, or video meeting, giving the employee no independent way to verify the request.
Artificial intelligence makes the first element—authority—substantially easier to fake. An employee may no longer receive only a suspicious email purportedly from the CEO; they may hear the CEO’s voice or see what appears to be the CEO on a video call.
This shifts a key assumption underlying many existing business processes: recognition is not verification. Organizations should design their procedures accordingly.
Five Controls Businesses Should Consider
1. Independently Verify Sensitive Requests
Requests to send money, disclose sensitive information, or change payment instructions should be verified through a second, trusted channel. If the request arrives by email, text, phone, or video, contact the requester using information already in your records—not the contact information contained in the incoming request. The key is independence: verification through the same potentially compromised channel is not meaningful verification.
2. Require Dual Authorization for Significant Payments
No single individual should be able to both initiate and release a significant payment. Where possible, configure this requirement within the organization’s banking platform rather than relying solely on written policy. A technical control requiring dual authorization is harder to bypass during a rushed transaction.
3. Independently Confirm Changes to Payment Instructions
Changes to wire or ACH instructions deserve particular scrutiny. When a client, vendor, title company, or other business partner provides new payment instructions, confirm the change verbally with a known contact using information already on file before releasing funds. A convincing email, familiar voice, or realistic video should not replace that verification step.
4. Create an Escalation Rule for Unusual Requests
Urgency should trigger more verification, not less. Codify that principle in policy. Requests involving unusual secrecy, significant amounts, new accounts, changed payment information, or departures from normal procedure should automatically receive additional review. Employees should know exactly whom to contact when something does not feel right.
5. Review Bank Procedures and Insurance Coverage
Organizations should understand the security procedures in their banking agreements and confirm that employees are following them. Businesses should also review insurance coverage to determine whether—and to what extent—their policies cover social engineering, impersonation fraud, or similar losses. Discovering policy exclusions before an incident is far more useful than discovering them after.
The Control That Makes the Others Work
There is another element that policy and technology alone cannot address: culture. Deepfake fraud succeeds in part because employees are conditioned to respond to authority.
Consider an accounts payable employee receiving an urgent call that sounds exactly like the CEO: I need this wire out before 5:00. I’m heading into a meeting. Just take care of it.
The employee may know the verification procedure. The harder question is whether they feel comfortable saying: Absolutely—I just need to verify it first.
This is a leadership issue. Executives, owners, officers, and directors should explicitly tell employees that verification is expected—even when the request appears to come from them—and reinforce that message when someone actually follows through.
An employee who slows down a legitimate transaction by following the verification process did not create a problem—the process worked.
Test the Process Before Someone Else Does
A written policy is only the beginning. Run a brief tabletop exercise with employees most likely to encounter these requests—finance and accounts payable personnel, executive assistants, receptionists, paralegals, and others who handle payments or sensitive information.
Present a realistic scenario: An executive calls late in the afternoon with an urgent transaction. The voice sounds right, the caller knows details about the company, and the money needs to move immediately. Then walk through what happens next.
Who verifies the request, and how? Who can stop or approve the payment? What happens if the executive insists there is no time? The exercise need not be elaborate—its purpose is to identify where procedures hold and where authority or urgency causes them to break down.
Start With the Basics
Organizations do not need to overhaul every security procedure because of deepfakes. A practical starting point is to review the transactions where impersonation would pose the greatest risk and ensure those transactions require independent verification.
The technology behind fraud is becoming more sophisticated, but the response does not always have to be. Sometimes the most effective control is simply a process in which no voice, image, email, or video can override verification.
For more information about Maryland’s new deepfake law, including the conduct it prohibits, criminal penalties and civil remedies available to victims, see our companion article, Maryland’s New Deepfake Fraud Law Takes Effect October 1: What Businesses Need to Know.
This article is for informational purposes only and does not constitute legal advice. Reading it does not create an attorney-client relationship.